WireGuard for Business: Use Cases, Limits, FIPS and Tailscale
WireGuard for business has gone from curiosity to serious option in a few years. WireGuard is a modern VPN protocol built around a tiny codebase, fixed modern cryptography and plain UDP transport — and that combination makes it fast, easy to audit and pleasant to operate, which is exactly what a busy network team wants.
It is not a drop-in replacement for every enterprise VPN feature, though, so the useful question is where it fits and what it needs around it.
What makes WireGuard different
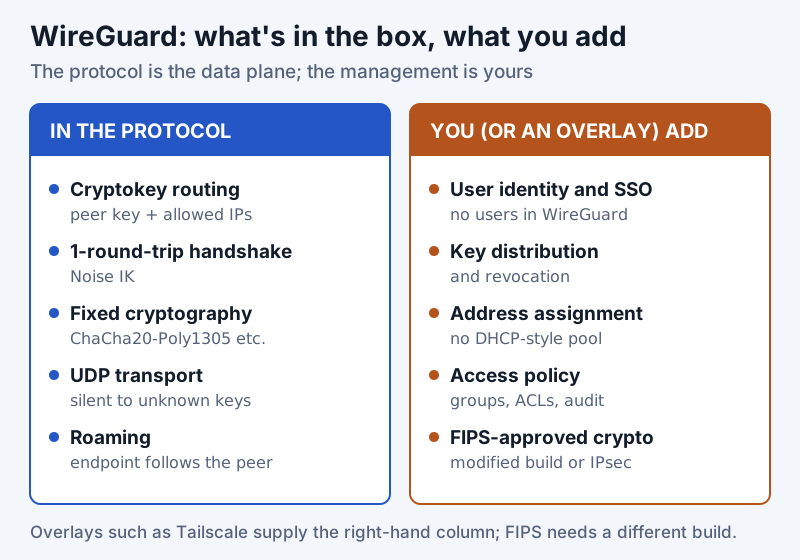
WireGuard's design choices are its selling points. Its codebase is on the order of a few thousand lines, small enough to audit, versus the hundreds of thousands in older stacks. It uses one fixed cipher suite rather than negotiating from a menu: ChaCha20 with Poly1305 for encryption, Curve25519 for key exchange, BLAKE2s for hashing and HKDF for key derivation, in a Noise IK handshake that takes one round trip. That removes a whole class of downgrade risks. It runs over UDP, and it has been in the mainline Linux kernel since version 5.6. The project's protocol notes are at wireguard.com.
The practical result is a tunnel that connects almost instantly, survives roaming well, and is simple enough that misconfiguration is less likely than with IPsec.
Where it is strong: site-to-site, remote access and mesh
WireGuard shines for fast site-to-site links between servers you control, for developer and admin access to cloud environments, and as the transport under a modern mesh network. Its speed and low overhead make it a good fit for connecting VPCs and data centres, and its simplicity lowers the operational cost of running your own VPN instead of buying one.
For teams weighing self-hosting, that last point is the real draw: a self-hosted WireGuard mesh gives you a modern VPN you fully control, with no per-seat licence and no third party in the trust path.
Where it needs help
WireGuard is deliberately minimal, so it leaves several enterprise concerns to you. It has no built-in user authentication or identity-provider integration — its identity model is static public keys, so you must manage key distribution and revocation yourself. It has no dynamic address assignment or central policy engine on its own. And because peers are pinned to keys, scaling to many roaming users means building configuration management around it.
None of these are flaws so much as scope decisions, but they mean bare WireGuard suits infrastructure and technical users better than a large non-technical workforce without additional tooling.
Where Tailscale fits
This is the gap Tailscale and similar tools fill. Tailscale builds on WireGuard for the data plane but adds the control plane WireGuard omits: it ties access to your identity provider, distributes keys automatically, handles NAT traversal, and lets you express access policy centrally. The result is a mesh VPN with the speed of WireGuard and the manageability a business needs.
If you want a fully self-owned option, run WireGuard directly; if you want WireGuard's benefits without building the control plane, Tailscale (or a comparable overlay) is the pragmatic path. Either way, weigh it against the more traditional options in VPN protocols compared for IT and the business VPN guide.
Compliance: WireGuard and FIPS 140-3
The fixed cipher suite that makes WireGuard simple is also its biggest compliance gap. ChaCha20-Poly1305, Curve25519 and BLAKE2s are not on NIST's list of approved algorithms, so a standard WireGuard set-up cannot run in a FIPS 140-3 validated mode. If your organisation must use FIPS-validated cryptography, as US federal systems and many of their contractors must, stock WireGuard is out.
There are two ways round it. Some vendors sell modified builds that swap in approved algorithms such as AES-GCM on a validated crypto module; the catch is that both ends must run the modified build, because it no longer speaks to standard peers. The other is to stay with IPsec where regulation dictates the algorithms. Even Tailscale, which is built on WireGuard, says IPsec suits environments where regulation, legacy operating systems or IoT devices dictate the encryption.
Firewalls and gateways that support WireGuard
You rarely need a separate server to try it. Several common business firewalls and gateways ship WireGuard or offer it as an add-on:
| Platform | How WireGuard is provided | Worth knowing |
|---|---|---|
| OPNsense | Built into the base system since 24.1 (January 2024) | Runs as a FreeBSD kernel module |
| pfSense Plus and CE | Add-on package from the Package Manager | Netgate notes it has no user authentication |
| MikroTik RouterOS 7 | Native interface | Default listen port 13231 |
| UniFi gateways | WireGuard VPN server in the Network application | Default port UDP 51820; needs a public IP |
Big enterprise firewalls from Fortinet, Cisco and Palo Alto Networks are built around IPsec and SSL VPN instead; we cover those in VPN protocols compared for IT.
How WireGuard actually connects
WireGuard's model is worth understanding because it explains both its strengths and its limits. Each peer has a key pair, and a peer's configuration lists the other peers by public key along with the IP ranges allowed through them — a scheme WireGuard calls cryptokey routing. There are no accounts and no negotiation menu; if a packet does not authenticate against a known key, it is silently dropped, so a WireGuard endpoint does not even announce itself to unauthenticated scanners.
The handshake is a fast, one-round-trip exchange, and connections are effectively stateless until traffic flows, which is why WireGuard reconnects instantly and roams cleanly between networks: when a peer sends a valid packet from a new address, the far end simply updates where it sends replies. That elegance is real, but notice what is missing — there is no user, no group and no central authority in the protocol itself, only keys and IP ranges. Managing those at human scale is the work an overlay takes off your hands.
The real business case: cost and control
For a business, WireGuard's appeal is ownership. A self-hosted WireGuard mesh has no per-seat licence, keeps the entire trust path inside your control, and runs on hardware or cloud instances you already have. For an infrastructure team connecting servers, environments and a modest number of technical users, that can be dramatically cheaper and simpler than a commercial VPN.
The cost you take on is operational: you own key distribution, revocation, IP allocation and access policy. That is fine at small or technical scale and painful at large or non-technical scale — which is exactly the boundary where a managed overlay earns its keep. If building and maintaining that control plane would cost more than a subscription, a tool like Tailscale (or a self-hosted coordination server) is the better trade, and we say so despite it earning us nothing.
The bottom line
WireGuard has earned its place in the enterprise toolbox, but it rewards matching it to the right job. For server-to-server links, cloud connectivity, developer access and modern mesh networks, its speed, small attack surface and low operational overhead are hard to beat, and self-hosting gives you a VPN with no per-seat cost and no third party in your trust path.
For a large, non-technical workforce that needs central identity, group policy and easy onboarding, bare WireGuard is not enough on its own — and that is not a criticism, just the boundary of what it set out to do. Pair it with an overlay that adds the control plane, or use a firewall's IPsec and SSL VPN features where those integrations already exist. The honest recommendation is to reach for WireGuard first where you control the endpoints, and to add management only where the scale actually demands it.
Frequently asked questions
Is WireGuard good for business use?
What are WireGuard's limitations for enterprises?
What is the difference between WireGuard and Tailscale?
Is WireGuard secure?
How does WireGuard identify peers?
Is WireGuard FIPS compliant?
Which business firewalls support WireGuard?
Start with the business VPN guide, or read how IPsec VPNs work in detail.